Account Takeover Prevention: Explained
Introduction (Account Takeover Prevention Explained)
Account Takeover Prevention Explained is a topic worth understanding well. Account takeover (ATO) is a growing threat that sees attackers hijack legitimate user accounts by stealing credentials or exploiting system weaknesses. According to Vectra, ATO attacks surged 250% in 2024, underscoring the urgency for robust defenses. Prevention is not a single tool but a layered strategy that combines user education, technology, and process controls. Effective ATO protection balances security with user experience, ensuring legitimate customers are not unduly inconvenienced. In this guide, we unpack the core components of ATO defense, illustrate how they work in practice, and show how organizations can weave them into their security fabric.
How Attackers Gain Control
Most ATO incidents start with credential compromise, often via phishing, credential stuffing, or malware. Once an attacker has a username and password, they may bypass traditional authentication by exploiting weak MFA, session hijacking, or social engineering. Cloudflare notes that attackers can also leverage stolen tokens or session cookies, making detection harder.
Foundational Controls
Strong Authentication
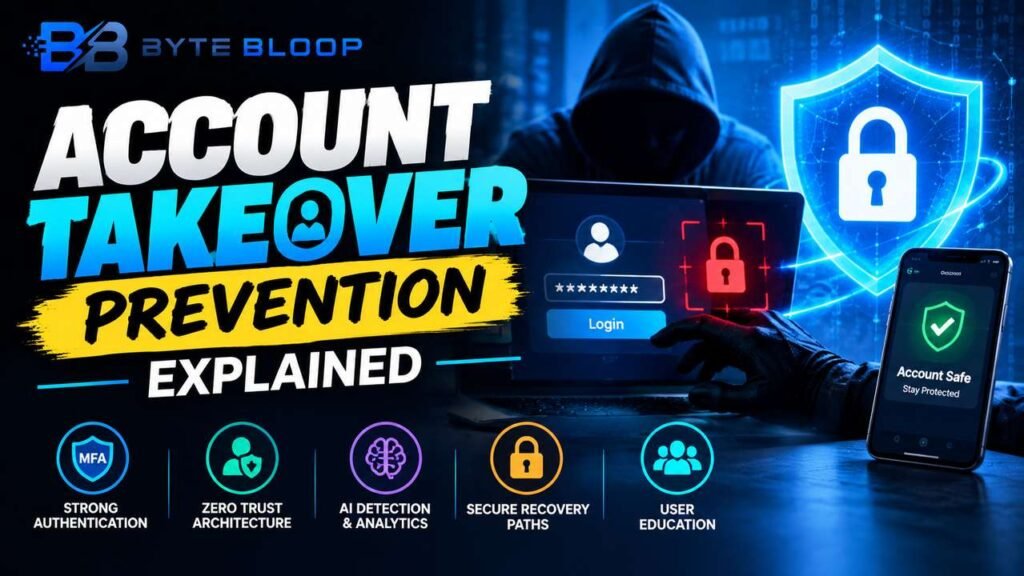
Multi‑factor authentication (MFA) remains the frontline defense. However, not all MFA is equal. Phishing‑resistant methods such as FIDO2/WebAuthn or hardware tokens significantly reduce the risk of credential theft. Imperva highlights that organizations that enforce MFA see a 90% drop in successful ATO attempts.
This matters directly for anyone exploring account takeover prevention explained.
Zero Trust Architecture
Zero Trust treats every access request as potentially hostile, verifying identity and context before granting permissions. By continuously monitoring device health, location, and behavior, systems can flag anomalous logins that deviate from a user’s normal pattern.
Getting account takeover prevention explained right can make a real difference.
Account Hygiene
Regularly prompting users to update passwords, removing unused devices, and enforcing password complexity limits the attack surface. Salt Security recommends a policy that requires password changes every 90 days for high‑risk accounts.
That is a core part of understanding account takeover prevention explained.
Behavioral Analytics & Detection
AI‑powered analytics can spot subtle deviations—like a sudden login from a new country or atypical transaction volume—that human monitoring might miss. Vectra’s guide stresses that combining behavioral signals with traditional rule‑based alerts yields the highest detection rates. Fingerprint’s 2026 list of detection tools shows that solutions integrating device fingerprinting and risk scoring are most effective.
Many readers look into account takeover prevention explained for exactly this reason.
Operational Measures
Account Lockout Policies
Implementing adaptive lockout thresholds—locking an account after a small number of failed attempts but allowing recovery via secure channels—helps thwart brute‑force attacks without locking out legitimate users.
It is worth revisiting account takeover prevention explained as things develop.
Recovery Path Security
Secure account recovery processes are critical. Using out‑of‑band verification (e.g., SMS to a verified phone number) or knowledge‑based questions that are hard to guess reduces the chance of an attacker resetting passwords.
Account Takeover Prevention Explained remains highly relevant here.
Employee Training
Human factors often remain the weakest link. Regular phishing simulations and clear reporting channels empower staff to spot and report suspicious activity before it escalates.
This is a key consideration when it comes to account takeover prevention explained.
Compliance and Reporting
Many industries mandate ATO protection under regulations such as GDPR, PCI‑DSS, and the NIST Cybersecurity Framework. SHIELD’s guide notes that a documented ATO strategy not only meets compliance but also builds customer trust.
Putting It All Together
An effective ATO defense is a holistic program: enforce strong MFA, adopt Zero Trust, apply behavioral analytics, secure recovery paths, and maintain rigorous user education. By layering these controls, organizations can detect and stop attacks early, minimizing financial loss and reputational damage.
Key Takeaways
- Phishing‑resistant MFA cuts ATO risk by up to 90%
- Zero Trust continuously verifies context, not just identity
- AI‑driven behavioral analytics spot anomalies missed by rule‑based alerts
- Secure recovery paths prevent attackers from resetting passwords
- Regular user education reduces human‑factor vulnerabilities
Frequently Asked Questions
What is account takeover and why is it dangerous?
Account takeover occurs when an attacker gains unauthorized control of a legitimate user’s account, often by stealing credentials. It can lead to data theft, financial loss, and reputational damage.
What are the key features of a robust ATO prevention strategy?
Strong MFA, Zero Trust architecture, behavioral analytics, secure recovery mechanisms, adaptive lockout policies, and ongoing user education.
What are the best use cases for AI‑driven detection in ATO protection?
AI excels at spotting subtle behavioral deviations, such as unusual login locations or transaction patterns, enabling real‑time alerts before an attacker fully compromises an account.
What are the pros and cons of enforcing strict MFA on all accounts?
Pros: dramatically reduces credential‑based attacks and builds customer trust. Cons: can introduce friction for users, potentially impacting adoption if not implemented with user‑friendly methods like hardware tokens.
Conclusion
Based on the available information and industry analysis, account takeover prevention is a multi‑layered discipline that blends technology, process, and people. By combining phishing‑resistant MFA, Zero Trust principles, AI‑powered behavioral analytics, and secure recovery workflows, organizations can detect and stop ATO attacks before they cause damage. The result is a resilient security posture that protects both business assets and customer trust.
Related Reading
- Zero Trust Architecture: A Beginner’s Guide
- Choosing the Right MFA Solution for Your Business
Sources & References
- A Practical Guide to Account Takeover Prevention
- Account Takeover Protection | Mitigate Account Fraud
- Account Takeover (ATO): How Attacks Work & Prevention
- Account Takeover Prevention – ATO Protection Best Practices
- The 13 Best Account Takeover Detection Tools in 2026
- A Strategic Guide to Account Takeover (ATO) Fraud … – SHIELD
- What Is Account Takeover Fraud? A Comprehensive Guide
- What is account takeover?
Related Articles