Wi‑Fi Security: Explained
Introduction
Wi‑Fi security is the backbone of modern connectivity, safeguarding the data that travels between your devices and the internet. Without robust protection, every packet sent over a wireless network becomes a potential target for eavesdroppers, hackers, and opportunistic attackers. At its core, Wi‑Fi security relies on encryption, authentication, and integrity checks to keep unauthorized users out and data confidential. The evolution from WEP to WPA3 reflects the industry’s response to increasingly sophisticated threats, each iteration adding stronger encryption and more resilient handshake mechanisms. For home users, a properly configured router can prevent casual snooping; for businesses, a layered approach—combining WPA3, guest VLANs, and network segmentation—is essential to defend against targeted attacks. Understanding the terminology, protocols, and practical steps to secure a wireless network is therefore critical for anyone who relies on Wi‑Fi for everyday life or commerce. In this guide, we break down the key concepts, compare the major protocols, and provide actionable steps to harden your network against common attacks.
What Wi‑Fi Security Actually Protects
According to SecureW2, Wi‑Fi security protects both the data in transit and the devices that connect to the network. By encrypting traffic, it ensures that even if an attacker intercepts packets, they cannot decipher the content. Authentication prevents unauthorized devices from joining, while integrity checks detect tampering. Without these safeguards, any device within range could connect to the network, potentially gaining access to shared files, printers, or even the router itself.
Evolution of Wi‑Fi Security Protocols
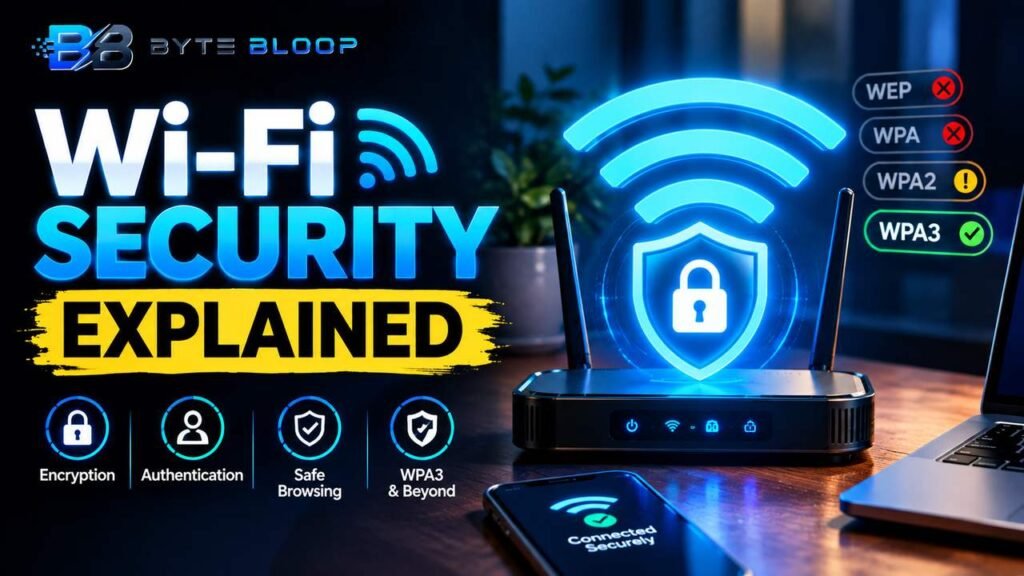
Early Wi‑Fi networks used WEP, which offered weak encryption and was easily cracked. The industry replaced it with WPA in 2003, adding TKIP for improved security, but WPA still had vulnerabilities. WPA2, introduced in 2004, brought AES encryption, a significant leap forward. However, WPA2’s pre‑shared key (PSK) mode was susceptible to offline dictionary attacks. In 2018, WPA3 addressed these gaps with the Simultaneous Authentication of Equals (SAE) handshake, stronger encryption, and mandatory protection for open networks via Opportunistic Wireless Encryption (OWE).
WPA3 Key Features
- SAE handshake eliminates offline dictionary attacks.
- 256‑bit encryption for enterprise networks.
- OWE provides encryption even on open networks.
- Improved protection against brute‑force attacks on weak passwords.
While WPA3 is the latest standard, many routers still ship with WPA2 as the default. Transitioning to WPA3 requires compatible devices; otherwise, dual‑mode operation may be necessary.
Common Threats to Wireless Networks
Even with encryption, attackers can exploit weaknesses in configuration or device firmware. Avast notes that attackers often use “Evil Twin” access points to mimic legitimate networks, tricking users into connecting and harvesting credentials. Rogue routers can also be set up to intercept traffic. Phishing attacks may target users who connect to unsecured public Wi‑Fi, leading to credential theft. Malware can spread via network shares if authentication is lax.
Practical Steps for Home Users
1. Change Default Credentials. Most routers ship with generic usernames and passwords; changing them immediately reduces risk.
2. Enable WPA3 (or WPA2‑AES). Check your router’s firmware; if WPA3 is available, enable it. If not, disable WEP and WPA.
3. Use a Strong Passphrase. Avoid dictionary words; combine letters, numbers, and symbols. Consider a passphrase generator.
4. Update Firmware Regularly. Manufacturers patch security flaws; install updates as soon as they’re released.
5. Segment Guest Networks. Create a separate SSID for visitors, limiting access to shared resources.
6. Disable Remote Management unless you need it, and if you do, secure it with a strong password and two‑factor authentication.
Business‑Grade Security Practices
For enterprises, security extends beyond the router. ECCouncil recommends a layered approach: separate VLANs for different departments, robust authentication via 802.1X, and regular penetration testing. Cloud‑managed Wi‑Fi solutions can automate policy enforcement and provide real‑time threat intelligence. Network monitoring tools should flag anomalous traffic, such as devices attempting to connect with unfamiliar MAC addresses.
Key Recommendations
- Implement WPA3 with enterprise‑grade authentication.
- Use network segmentation to isolate sensitive traffic.
- Deploy intrusion detection systems (IDS) tuned for wireless anomalies.
- Educate employees on phishing and social engineering.
Future Trends in Wi‑Fi Security
Wi‑Fi 6E and 7 will bring higher throughput and new security features, but the core principles of encryption and authentication remain. Researchers are exploring post‑quantum cryptography to prepare for quantum‑computing threats. Meanwhile, zero‑trust networking models are gaining traction, treating every device as potentially compromised and enforcing continuous verification.
Key Takeaways
- WPA3’s SAE handshake blocks offline dictionary attacks
- Strong, unique passphrases are essential for all networks
- Regular firmware updates patch critical vulnerabilities
- Guest networks should be isolated from corporate traffic
- Zero‑trust models add an extra layer of protection
Frequently Asked Questions
What is Wi‑Fi security explained?
Wi‑Fi security explains how encryption, authentication, and integrity checks protect wireless networks from unauthorized access and cyber threats.
What are the key features of WPA3?
WPA3 introduces the SAE handshake to block offline attacks, offers 256‑bit encryption for enterprise, and provides Opportunistic Wireless Encryption for open networks.
What are the best use cases for a guest network?
Guest networks allow visitors to access the internet without exposing internal resources, ideal for homes, cafés, and corporate visitor access.
What are the pros and cons of WPA2 versus WPA3?
WPA2 is widely supported and provides AES encryption, but is vulnerable to offline dictionary attacks; WPA3 offers stronger security but requires newer hardware and may need dual‑mode support.
Conclusion
Based on the available information and industry analysis, Wi‑Fi security provides the foundational protection necessary for both personal and professional networks, ensuring that data remains confidential and devices remain authenticated. By adopting modern protocols like WPA3, maintaining robust passphrases, and staying vigilant against emerging threats, users can confidently rely on wireless connectivity without compromising safety.
Related Reading
- How to Choose the Right Router for Your Home
Sources & References